
Every Command Inspected
Before It Runs.
Binary Armor can be integrated inline, inspecting data packets in real time with minimal latency. Unauthorized commands never reach your equipment.
/ SCADA
Sent
Approved
Critical Device
Deep Packet Inspection
Parses every byte of every protocol message, not just the headers.
Functional Whitelisting
Checks each command against your policy: the right source, target, values and operating state.
A layer your security stack doesn't have yet.
A solid security posture relies on layers of defense, with each layer designed to catch what the previous one missed. At Purdue Levels 0 and 1, protection goes from limited to none. A command that reaches a controller executes, and a valve opens or a breaker trips. Binary Armor can be integrated inline at exactly that point and enforces your rules on commands before they execute. It complements the stack you already run.
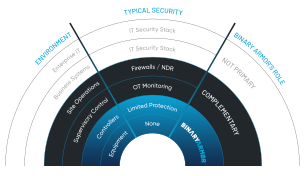
Four Reasons OT Teams Choose Binary Armor.
Active, Not Passive
Enforces your rules on commands before they execute, not after the alert.
Independently Certified
Common Criteria certified and DODIN APL listed. Independently tested, not vendor-attested.
No Infrastructure Change
Installs bump-in-wire between existing devices. No agents, no reconfiguration, no downtime to deploy.
A New Layer, Not a Replacement
Operates at Purdue Levels 0 through 2, adding command-level enforcement alongside the products you already run.
Where Binary Armor Works
Industries We Protect
 Energy & Utilities
 Defense & Aerospace
 Water & Wastewater
 Critical Manufacturing
 Telecommunication
 Transportation
 Oil & Gas
 Healthcare
Defense In Depth
Why every layer needs the others
Binary Armor Fills the Gap
Between Detection & Prevention
Prevention stops threats before they touch your systems
Binary Armor
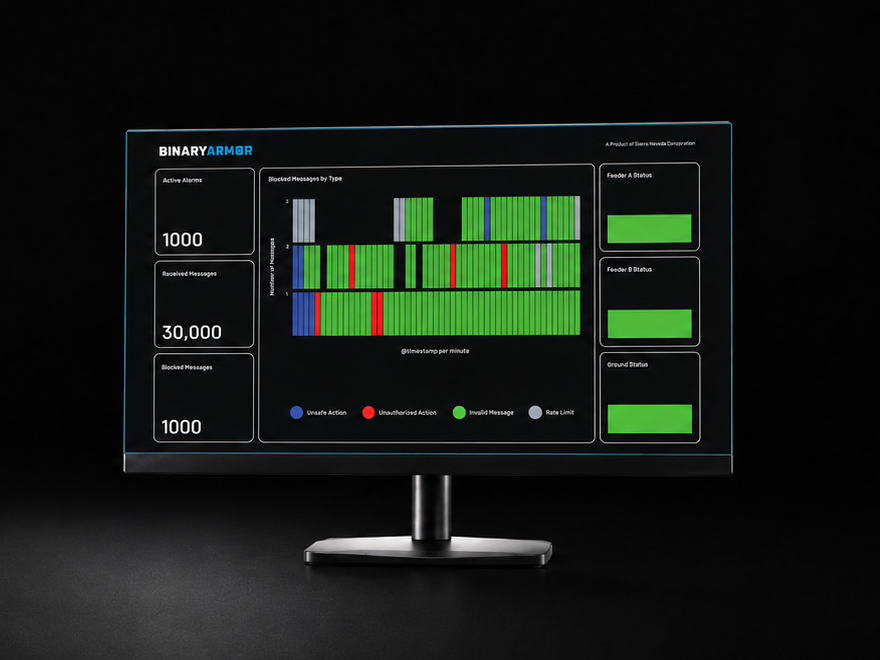
Blocks commands before execution
Visibility Products
Alerts after damage occurs
Protocols & Deployment Options
Supported ICS Protocols
Available Form Factors
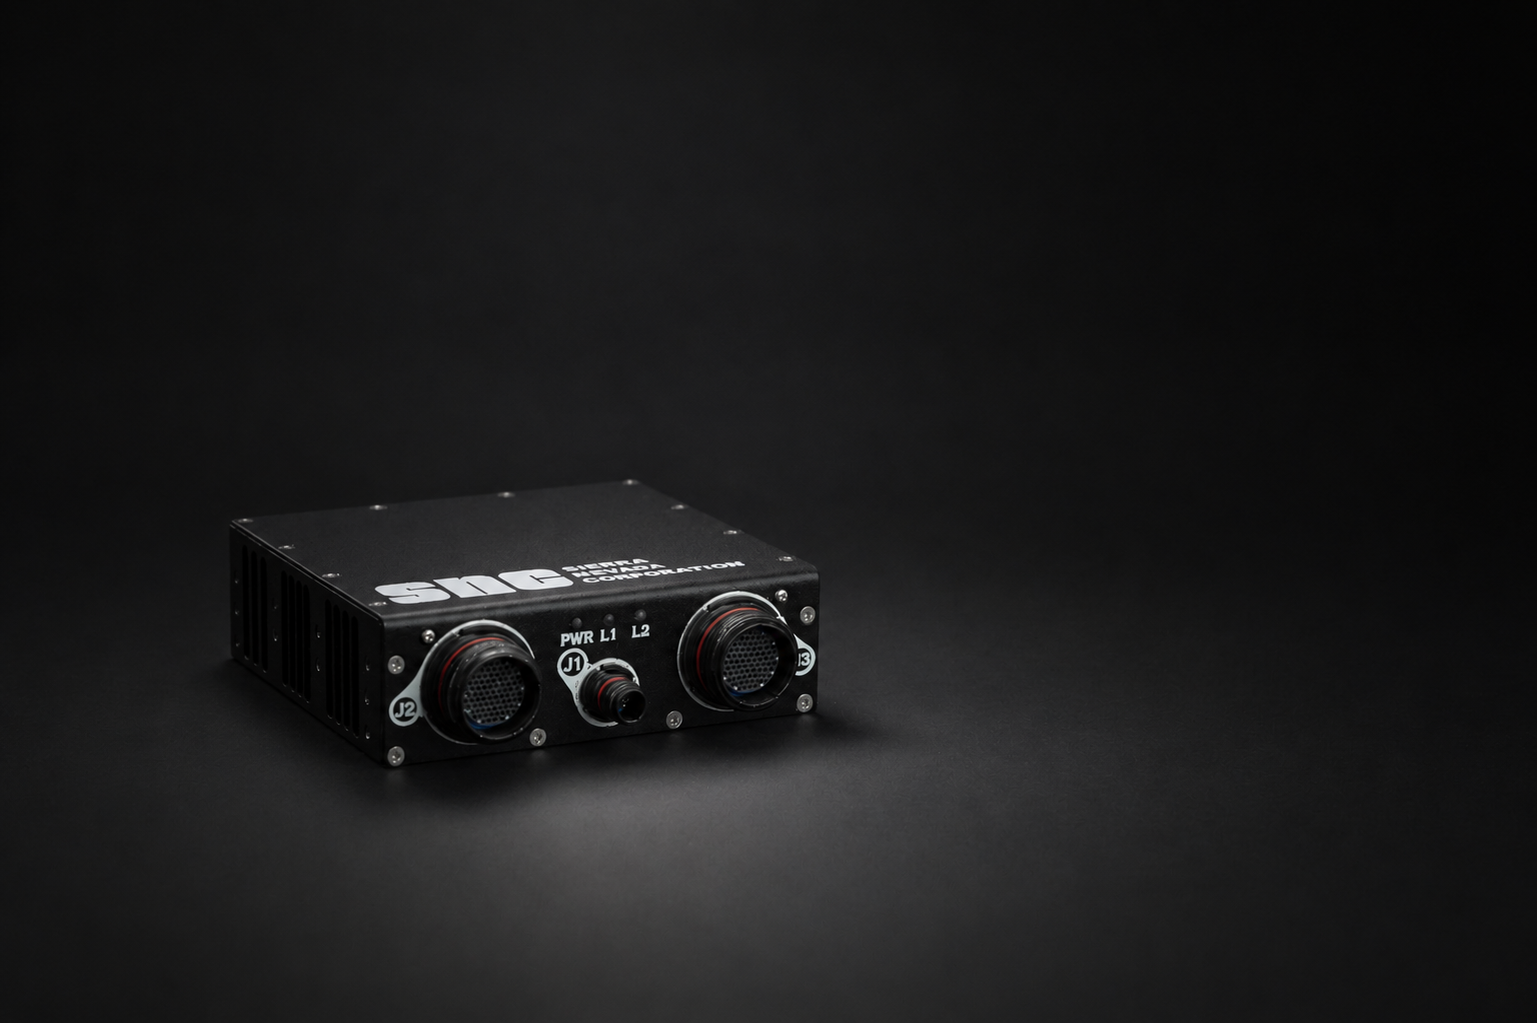
Ruggedized, DIN-rail mount, –40°C to +85°C rated
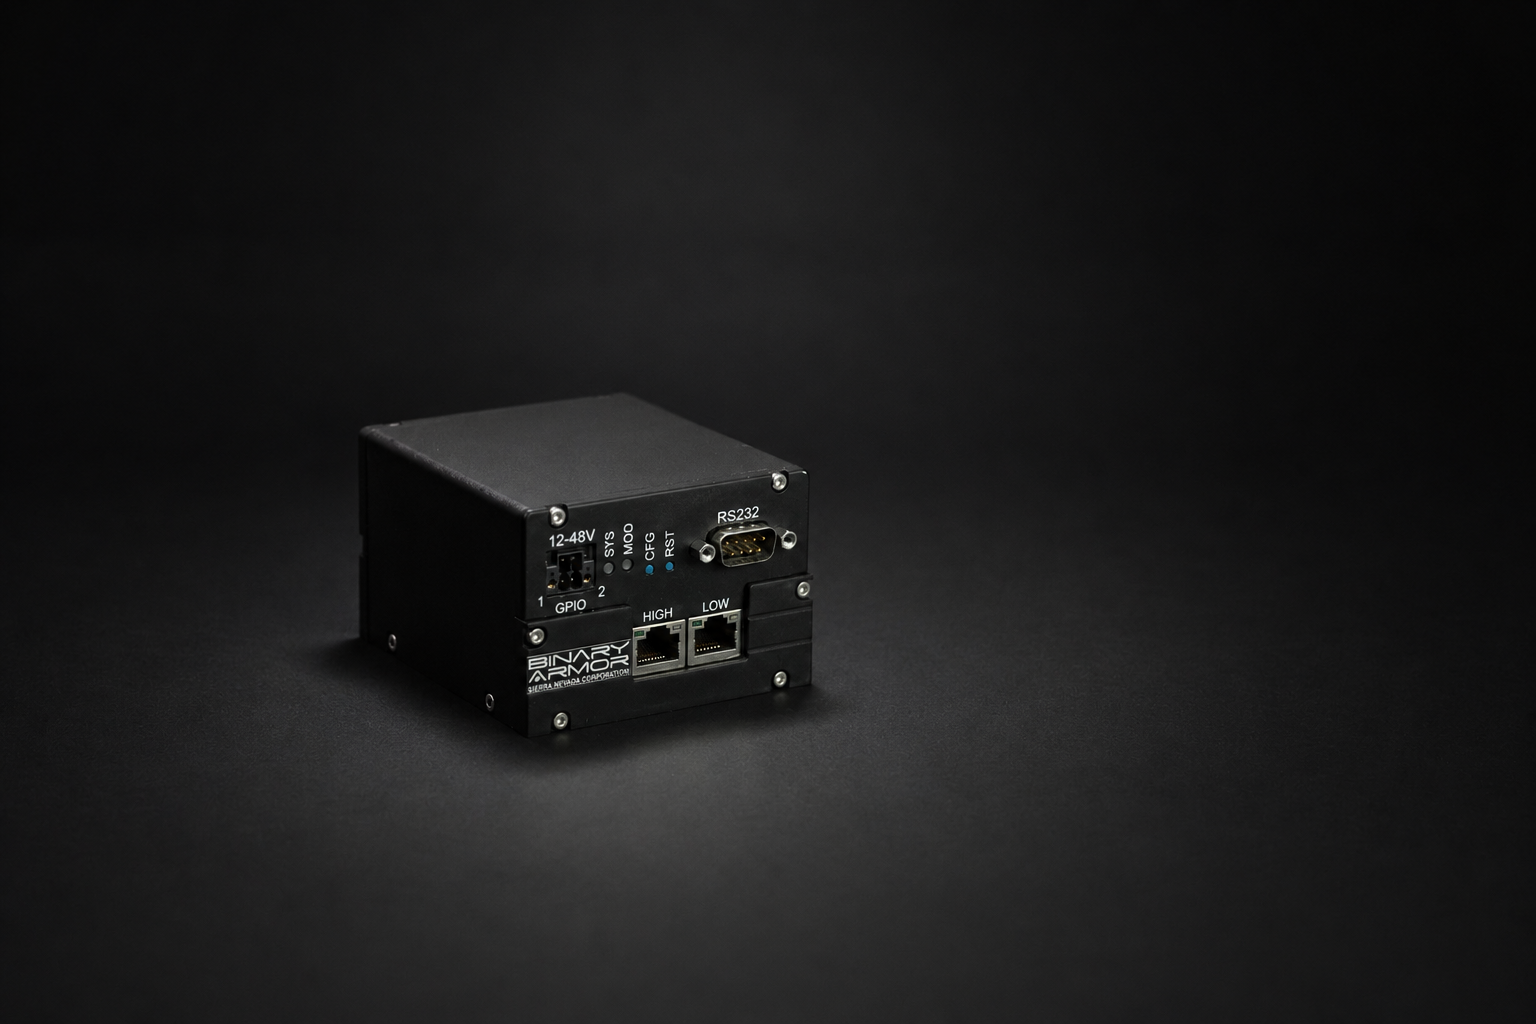
Deploy on existing hardware or virtual machines
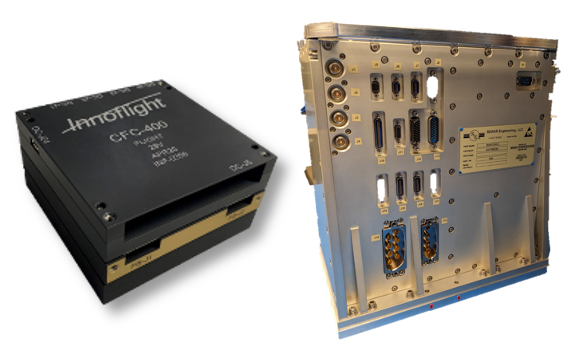
Airborne OT protection for defense platforms
Satellite OT protection validated on-orbit May 2025
Download Spec Sheets
Request Received
Questions
Get answers about integrating Binary Armor into your operational environment
Binary Armor operates across industrial control systems, SCADA networks and space-based infrastructure. It integrates with existing OT environments without requiring complete system overhauls. Compatibility assessments determine the best deployment approach for your specific assets.
Monitoring can begin on day one. The Binary Armor team can establish baseline patterns during week one. Upon review of the baseline, full defensive capability within the first month. Threat intelligence continues strengthening your defenses as the system learns your operational landscape.
Binary Armor can be deployed with minimal infrastructure modifications. Binary Armor is typically integrated between command sources and critical systems, observing and validating without disrupting existing workflows. Operations continue running while protection takes hold.
Command validation happens in real time with negligible latency. Binary Armor’s architecture ensures authorized operations proceed at normal speed while unauthorized commands face immediate rejection.
Maintenance is handled with minimal operational disruption. Your team receives regular reports on blocked threats and system performance metrics.
Protect Your
Operations Today
Request a demonstration and discover how Binary Armor secures your critical assets
Request a Demo